 Charles Lyons-Burt
- DFARS and NIST 800-171 obligations remain unchanged despite the CMMC pause
- Aethon Security offers CMMC compliance in as few as 30 days, starting at $22,500
- A pending FAR rule would extend NIST 800-171 requirements government-wide
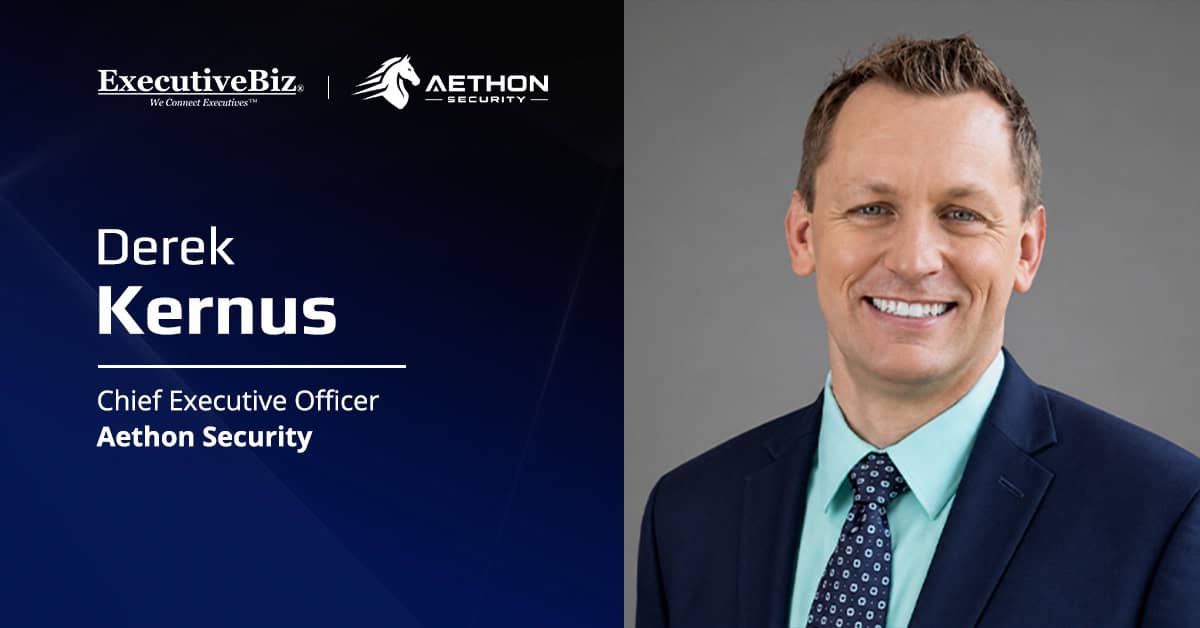
Derek Kernus‘ path into government contracting started with a detour. He joined the military in the early 2010s intending to build a career in service, but a physical injury cut that plan short. He went back to school instead, earning his master’s degree, with his sights set on breaking into government contracting. That effort led to an internship at a government contractor in 2019 — the entry point for what has become a career spent helping the defense industrial base make sense of its cybersecurity obligations. Today, Kernus serves as CEO of Aethon Security, a managed service provider he built to guide contractors through the Cybersecurity Maturity Model Certification landscape.
Kernus spoke with ExecutiveBiz about what the current pause in CMMC assessment activity does and doesn’t change, the cost misconceptions holding small businesses back from compliance, and where he expects cybersecurity requirements to head next.
ExecutiveBiz: The CMMC assessment requirements may be paused, but the cybersecurity requirements themselves are not. What is the biggest misconception defense contractors have right now?
Derek Kernus: In reality, the contractor’s obligations haven’t changed. The original regulation, DFARS 252.204-7012 for safeguarding controlled unclassified information, or CUI, is still in effect, and so is full compliance with NIST SP 800-171 — the cybersecurity requirements portion of that regulation. Self-assessments and reporting scores via the Supplier Performance Risk System, or SPRS, are still required. The biggest misconception is that some contractors feel they no longer need to address NIST 800-171, or that they can wait.
That’s especially risky for subcontractors. There’s still a lot of value in being compliant with the requirements, and even in being third-party certified, because primes are weighing a company’s cybersecurity posture when building a bid or awarding a subcontract to their team members. This can be a major differentiator when working with teaming partners. Contracting officers, under DFARS 252.204-7024, are also taking SPRS scores into consideration when making awards, so contractors need to make sure they’re documenting their posture in SPRS.
EBiz: America’s defense supply chain depends on small, innovative companies, yet many of these organizations struggle with the cost, expertise and operational burden associated with cybersecurity and compliance. What are the biggest challenges these businesses face?
Kernus: The biggest challenge is that they just don’t know what they don’t know about the requirements. They don’t live in this world every single day. Working with a partner helps them understand exactly what’s needed and exactly where their gaps are, and whether they actually need help maintaining these requirements moving forward.
The real issue underneath all of it is the security of the innovative technology these companies are creating for the defense industrial base. Leading technologies are left exposed through unsecured contractor systems, which hands adversaries an opportunity to study them, counter them, replicate them or improve on them — and move faster than we can. Innovations meant to give the U.S. a strategic advantage end up compromised before they can deliver value.
EBiz: And what is Aethon Security doing to make cybersecurity and CMMC more practical and affordable for those businesses?
Kernus: There are some big misconceptions about cost. Contractors hear that it can take years and cost hundreds of thousands of dollars to become compliant, and that simply isn’t true. Every situation is different, but companies like Aethon Security have built service offerings that let small, innovative companies achieve compliance in as few as 30 days and be certification assessment-ready in as few as 45 to 60 days, at a price as low as $22,500. That figure is also close to the annual cost of the three-year certification—the assessment cost gets amortized over that full three-year term.
From my perspective, the cost of compliance is absolutely affordable for small businesses. They need to take the time to research and talk with vendors to understand their operational and IT needs, since that’s the biggest driver of cost. But the cost of non-compliance is something our country simply can’t afford right now. Using managed service providers and partners like this actually helps reduce the overall cost of compliance, and we’re starting to see that dynamic take hold more broadly across the CMMC ecosystem.
EBiz: What should defense contractors be doing right now while the government continues to evaluate the future direction of the CMMC program?
Kernus: One thing they definitely shouldn’t be doing is stopping or waiting on implementing the requirements. In fact, the Information Security Oversight Office just published a notice saying the CUI program is moving forward full steam ahead, and that agencies and organizations need to make sure they’re implementing the requirements and flowing them down to the contracting base. As I mentioned, the requirements to address NIST 800-171 and the associated DFARS regulations haven’t changed and are still holding companies accountable. It’s still possible to get assessed by the Defense Industrial Base Cybersecurity Assessment Center, known as DIBCAC — the government’s version of a CMMC assessor. Companies that move forward and even continue to get certified during this evaluation period are in a very good spot with prime contractors.
Contractors should keep in mind that the review underway is happening at the prime level — that’s the relationship between the prime contractor and the government. But primes today still have to flow down the DFARS 7012 clause to their subcontractors, and a great way for a subcontractor to demonstrate those requirements are being implemented is by holding a Level 2 certification. We’re still seeing prime contractors require that today. There’s a real advantage for subcontractors in staying proactive while the Department of War continues to evaluate the program’s future direction. Bottom line: think of CMMC as a business acquisition strategy, still.
EBiz: As cyber threats continue to target agencies and departments across all of government and critical infrastructure, how will cybersecurity requirements expand beyond the defense industrial base?
Kernus: There’s currently a Federal Acquisition Regulation rule on controlled unclassified information that’s gone through two public comment periods and now sits with the Office of Management and Budget. I don’t believe it’s on the unified agenda yet, but the second round of public comments is being adjudicated, so major milestones have already been cleared. That rule would make full compliance with NIST 800-171 a requirement for all suppliers to all departments and agencies of the federal government handling CUI — not just the Department of War. That’s something every contractor needs to be paying attention to, because it’s a broader signal: this is coming everywhere.
EBiz: What lessons should policymakers take from the CMMC experience?
Kernus: They should understand that self-attestation has been ineffective, and that’s well documented — there are numerous Government Accountability Office reports and numerous internal department reports that make the case. Policymakers really need to move toward third-party enforcement. Trust but verify is essential to assuring companies put the safeguards in place necessary to protect the sensitive information they’ve been entrusted with.
EBiz: You mentioned third-party assessors. For readers who aren’t familiar, can you explain how the C3PAO ecosystem came together?
Kernus: Third-party assessor organizations exist in the FedRAMP world too — there they’re called 3PAOs, so it’s a similar structure. In the CMMC ecosystem, they’re called CMMC Third-Party Assessment Organizations, or C3PAOs. That ecosystem wasn’t stood up until the CMMC program itself was becoming a reality, and it was built by what’s now called The Cyber AB. The Cyber AB has a no-cost contract with the Department of War to maintain the CMMC ecosystem — they stood up all the requirements around becoming a C3PAO, including a code of ethics, among other things. None of that existed until CMMC became an official Department of War program.
EBiz: What changes could help reduce compliance costs and complexity while still achieving meaningful security improvements?
Kernus: There are certainly some efficiencies that could be built into the CMMC program. With the request for information response the department asked for, which closed about three weeks ago, I know quite a few individuals — myself included — suggested things like not requiring two assessors on every single assessment, and reducing other complexities. More clarity is also needed around what actually requires reassessment when a significant change occurs. Right now, the understanding is that a significant change triggers a full reassessment, but what’s still unclear in the CMMC FAQs is whether that means a self-assessment — even for an organization that’s already third-party certified — or a full reassessment by a C3PAO. It would help to instead assess only the delta, the controls relevant to that specific change, which would reduce cost and burden.
As for meaningful security improvements, that’s what transitioning to NIST SP 800-171 Revision 3 will do for the CMMC program, and the Department of War and Office of Management and Budget will determine that timeline. We shouldn’t be reducing the requirements given today’s threat environment, but we should be looking at the program itself and asking how to make adjustments that help assessors reduce the cost of assessment — and hopefully pass those savings along to contractors.
EBiz: Beyond serving clients, Aethon has been active across industry groups and the broader CMMC community. What role should service providers and ecosystem partners play as the program evolves?
Kernus: Education is key, and it starts with the contractors, the subcontractors and their suppliers. They’re typically not compliance experts, security experts or IT experts, and they don’t speak the acronym-laden language of government or compliance speak. We’ve heavily invested in translating that techno-babble into terms that make sense and practices companies can actually perform.
We’re also involved through the MSP Collective, formally known as MSPs for the Protection of Critical Infrastructure, in educating Congress, the Department of War and others in government — as well as other managed service providers — about the need to properly protect critical infrastructure, of which the defense industrial base is a part. It’s alarming how many people don’t understand the national security implications of programs like CMMC, don’t have accurate information about the cost for contractors and for government, or don’t understand the critical role MSPs like Aethon Security play in enabling companies in the DIB and other critical infrastructure sectors to affordably meet those security obligations.
Who Is Derek Kernus?
Kernus holds a B.S. and an M.B.A. from William & Mary’s Raymond A. Mason School of Business, with concentrations in process management, consulting and marketing. His technical background spans Azure, Azure Government, Microsoft 365 GCC High environments and a range of on-premises network architectures. He also holds the CISSP and CCSP certifications from ISC2 and is a Lead CMMC Certified Assessor.
His route into government contracting began with an internship in 2019, which grew into a senior consultant role focused on CMMC and NIST SP 800-171 readiness for Department of War supply chain contractors. He went on to serve as director of cybersecurity operations, overseeing organizational compliance objectives and a cybersecurity operations center, before becoming deputy chief information security officer at Sentinel Blue, where he managed client compliance programs and led updates to the firm’s CMMC Level 2 onboarding process.
Kernus founded Aethon Security in 2024 and has served as its chief executive officer since. He has since taken on an additional leadership role as chief executive officer of IVA’AL Solutions, LLC.
Who Is Aethon Security?
Aethon Security is a managed service provider focused on helping defense contractors reach and maintain CMMC certification. The company works with clients across the full compliance lifecycle, from initial readiness assessments through certification and ongoing maintenance, combining cybersecurity engineering, systems integration and documentation support so contractors can keep their attention on running their business and competing for new work.